Almost an hour just work especial bypass , and I found also , just enter the url http://127.0.0.1/fbip/ fill in the username with the query : 'Or 0 = 0 #
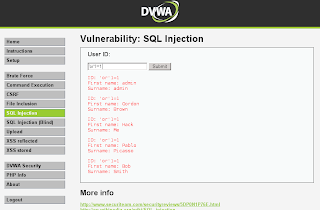
Still the spirit of course , we will try SQL injection technique this time , to the target itself is http://127.0.0.1/dvwa our first try with a standard query ' or'1 = 1